KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens

The Anatomy of the KREMLIN Campaign
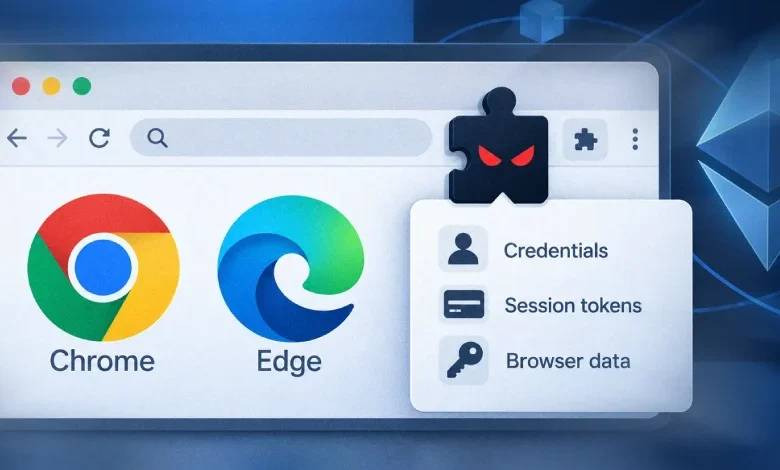
The KREMLIN ecosystem is a multi-stage infection framework designed for stealth and longevity. Its primary objective is the surreptitious installation of malicious browser extensions on Google Chrome and Microsoft Edge. By compromising these browsers, the attackers gain the ability to harvest sensitive user data, including banking credentials, session tokens, and multifactor authentication (MFA) codes, effectively bypassing standard security measures used by Brazilian financial institutions.
The infection chain begins with a social engineering lure. Victims are typically prompted to execute a JavaScript file disguised as a legitimate document—such as an invoice, a corporate contract, or a bank statement. Upon manual execution, the malware initiates a multi-stage loader. This loader is equipped with rigorous environmental checks; it will only proceed if it detects that it is not operating within a sandbox or a virtual machine. By analyzing system hardware—specifically CPU core counts and total RAM capacity—the malware ensures it is running on a genuine victim’s machine rather than an automated analysis platform.
Blockchain-Powered Command and Control
A defining feature that sets REF9334 apart from conventional threat actors is its reliance on Ethereum smart contracts. By hard-coding smart contract addresses into the malware, the attackers have effectively created a “dead drop” resolver system. This allows the threat actor to update their C2 server infrastructure and payload hosting locations in real-time without needing to recompile the malware or rely on static, easily sinkholed domain names.

If a primary domain is seized or identified by security vendors, the actor simply updates the Ethereum smart contract with new infrastructure addresses. The malware periodically queries these blockchain-based resolvers to receive its latest instructions, creating a resilient feedback loop that is exceptionally difficult for defenders to dismantle completely.
Chronology of Operations
The timeline of the KREMLIN campaign demonstrates a steady increase in operational complexity:
- May 2025: Initial observed activity of the REF9334 group, focusing on the distribution of off-the-shelf Trojans such as Pulsar RAT and Remcos RAT.
- June 16, 2025: Commencement of the first of seven distinct campaigns identified by security researchers, marking a shift toward more targeted financial fraud.
- May 19, 2026: A major pivot in operational strategy, during which the threat actor integrated Ethereum smart contract infrastructure into the malware’s core communication protocol.
- August 2026: Observed overlap in methodology with other threat actors, notably the Chinese-linked group APT31, which utilized similar browser-integrity bypass techniques to deploy the GemStone malware.
Technical Evasion and Persistence
The malware’s persistence mechanism is twofold. First, it establishes scheduled tasks on the infected Windows host to ensure execution upon system reboot. Second, it employs a sophisticated C++ installer that abuses legitimate software to facilitate side-loading. Specifically, the malware mimics the "SentinelAgentCore.dll," a component of the SentinelOne security platform, to execute its unsigned, malicious payload under the guise of a trusted security process.
To bypass Chromium’s integrity protections—specifically the "Secure Preferences" mechanism which monitors for unauthorized browser modifications—the malware utilizes techniques known as "Phantom Extension" and "GhostChrome-X." By manually editing the browser’s preference files and regenerating HMAC signatures, the malware registers its malicious extension as a legitimate, trusted component of the browser environment. Once installed, the extension, labeled "AVSync System Inc.," requests high-level permissions, including access to web requests, cookies, and local storage.

Global and Regional Impact
The scope of this campaign is heavily localized, with over 98% of identified victims residing within Brazil. Elastic Security Labs identified approximately 1,515 unique infected systems during their investigation into the group’s “network canary” check—a defense mechanism that causes the malware to crash if it detects a sandbox attempting to simulate network connectivity.
By registering the domain intended for this canary check, researchers were able to gain visibility into the scale of the infection. While the victims remain infected with the core malware, this intervention has effectively degraded the attacker’s ability to conduct automated sandbox evasion, providing security teams with a critical window of opportunity to remediate affected endpoints.
Broader Cybersecurity Implications
The rise of KREMLIN highlights a dangerous trend: the democratization of high-end, nation-state-style exploitation techniques among regional cybercriminal groups. The adoption of blockchain-based C2 infrastructure signals a move away from centralized, vulnerable command structures toward decentralized, hardened architectures.
Furthermore, the persistent targeting of browser integrity mechanisms suggests that browsers have become the most valuable real estate for modern threat actors. Because the browser acts as the gateway to nearly all modern financial, enterprise, and personal data, the ability to bypass integrity protections—even if temporary—allows for the total compromise of a user’s digital identity.

Analysis of Defensive Measures
The sophistication of the REF9334 group poses a significant challenge for traditional signature-based antivirus solutions. Because the malware resides in memory, utilizes legitimate process side-loading, and uses encrypted, decentralized infrastructure, it often flies under the radar of automated detection tools.
Security experts recommend that financial institutions and organizations operating in the region adopt a "defense-in-depth" approach. This includes:
- Hardening Browser Environments: Implementing enterprise-level policies that restrict the installation of browser extensions to only those explicitly approved via a whitelist.
- Endpoint Detection and Response (EDR): Focusing on behavioral analysis rather than file-based signatures. Detecting abnormal child-process creation, such as a browser process suddenly initiating unusual web requests or modifying its own configuration files, is vital.
- Network Monitoring: Monitoring for outbound traffic to known cryptocurrency-related domains or unusual endpoints that do not correspond to standard business traffic.
- User Awareness: Educating staff on the risks of executing unsolicited documents, particularly those masquerading as invoices or legal documents, remains the most effective front-line defense.
As the digital landscape in Brazil continues to evolve, the KREMLIN operation serves as a stark reminder of the adaptability of threat actors. The convergence of decentralized finance infrastructure with traditional malware distribution is likely to become a blueprint for future campaigns, necessitating a more proactive and intelligence-driven response from the global cybersecurity community. With the threat actor still active and the C2 infrastructure remaining resilient due to its blockchain-based design, the risk to financial integrity in the region remains high, requiring continued vigilance from both individual users and corporate security departments.